

Today, Aikido launches Noon.
We built Aikido to secure developers. But what about…everybody else?
Companies don’t just need to protect the software they build. They need to protect the people building it, too.
While we may not like to admit it, we are the most likely breach. Yes, we, humans. And it’s most likely to happen in the most mundane way, where we least expect it. Humans were involved in 62% of breaches in the last year. So while novel AI attacks and agent sandboxes monopolize budget and oxygen in the security discussion, someone in finance is opening StaffSalaries2026.xls.exe.
The bigger threat is still that urgent email invite to the company Christmas party asking you to RSVP via the link or lose your spot.
It's no longer just princes out there...
We can’t blame humans though. Phishing has gotten good. By and large, phishing no longer looks like phishing. It’s no longer just princes asking for money with obvious typos (I, too, need 5 iTunes gift cards for my cat’s surgery within the next 2 hours!!!). Today’s attackers are AI-native. Phishing campaigns are sophisticated, multi-channel, and armed with enough context to make it virtually impossible to tell what’s real and what’s fake. You get an email or a calendar invite, followed by a text about that email, then a call from someone who sounds exactly like your CFO.
Forty-one percent of social engineering breaches involved a channel other than email. Why? Because it works. Phone-based social engineering is about 40% more effective than email phishing.
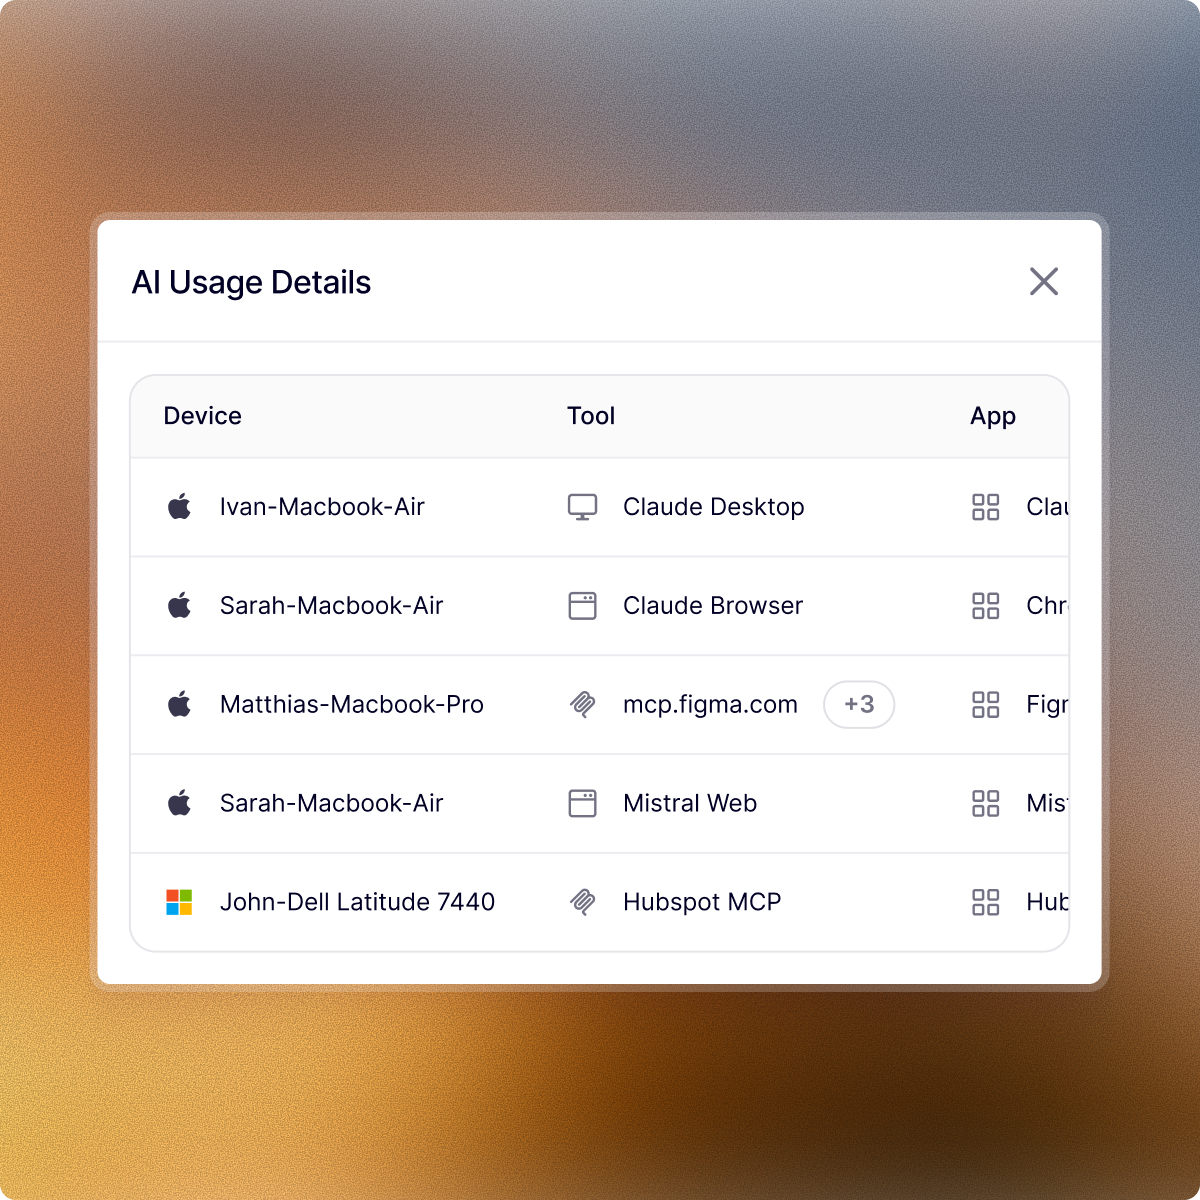
But impersonation is only part of it. Employees are installing AI tools, connecting MCP servers, and giving agents access to company systems and data. The proportion of employees who use AI regularly on corporate devices has tripled in one year. Every new tool, package, and agent skill introduces something else to secure.
Protecting your workforce now means understanding what people are installing, what their agents can do, and which tools can access company data. Alongside the inboxes, devices, and people you already needed to protect.
So there’s more to protect, and the attacks look more real. And it’s only getting worse. Much, much worse. AI makes attacks like these easier to create, personalize, and run at scale.
Which is why we built Noon
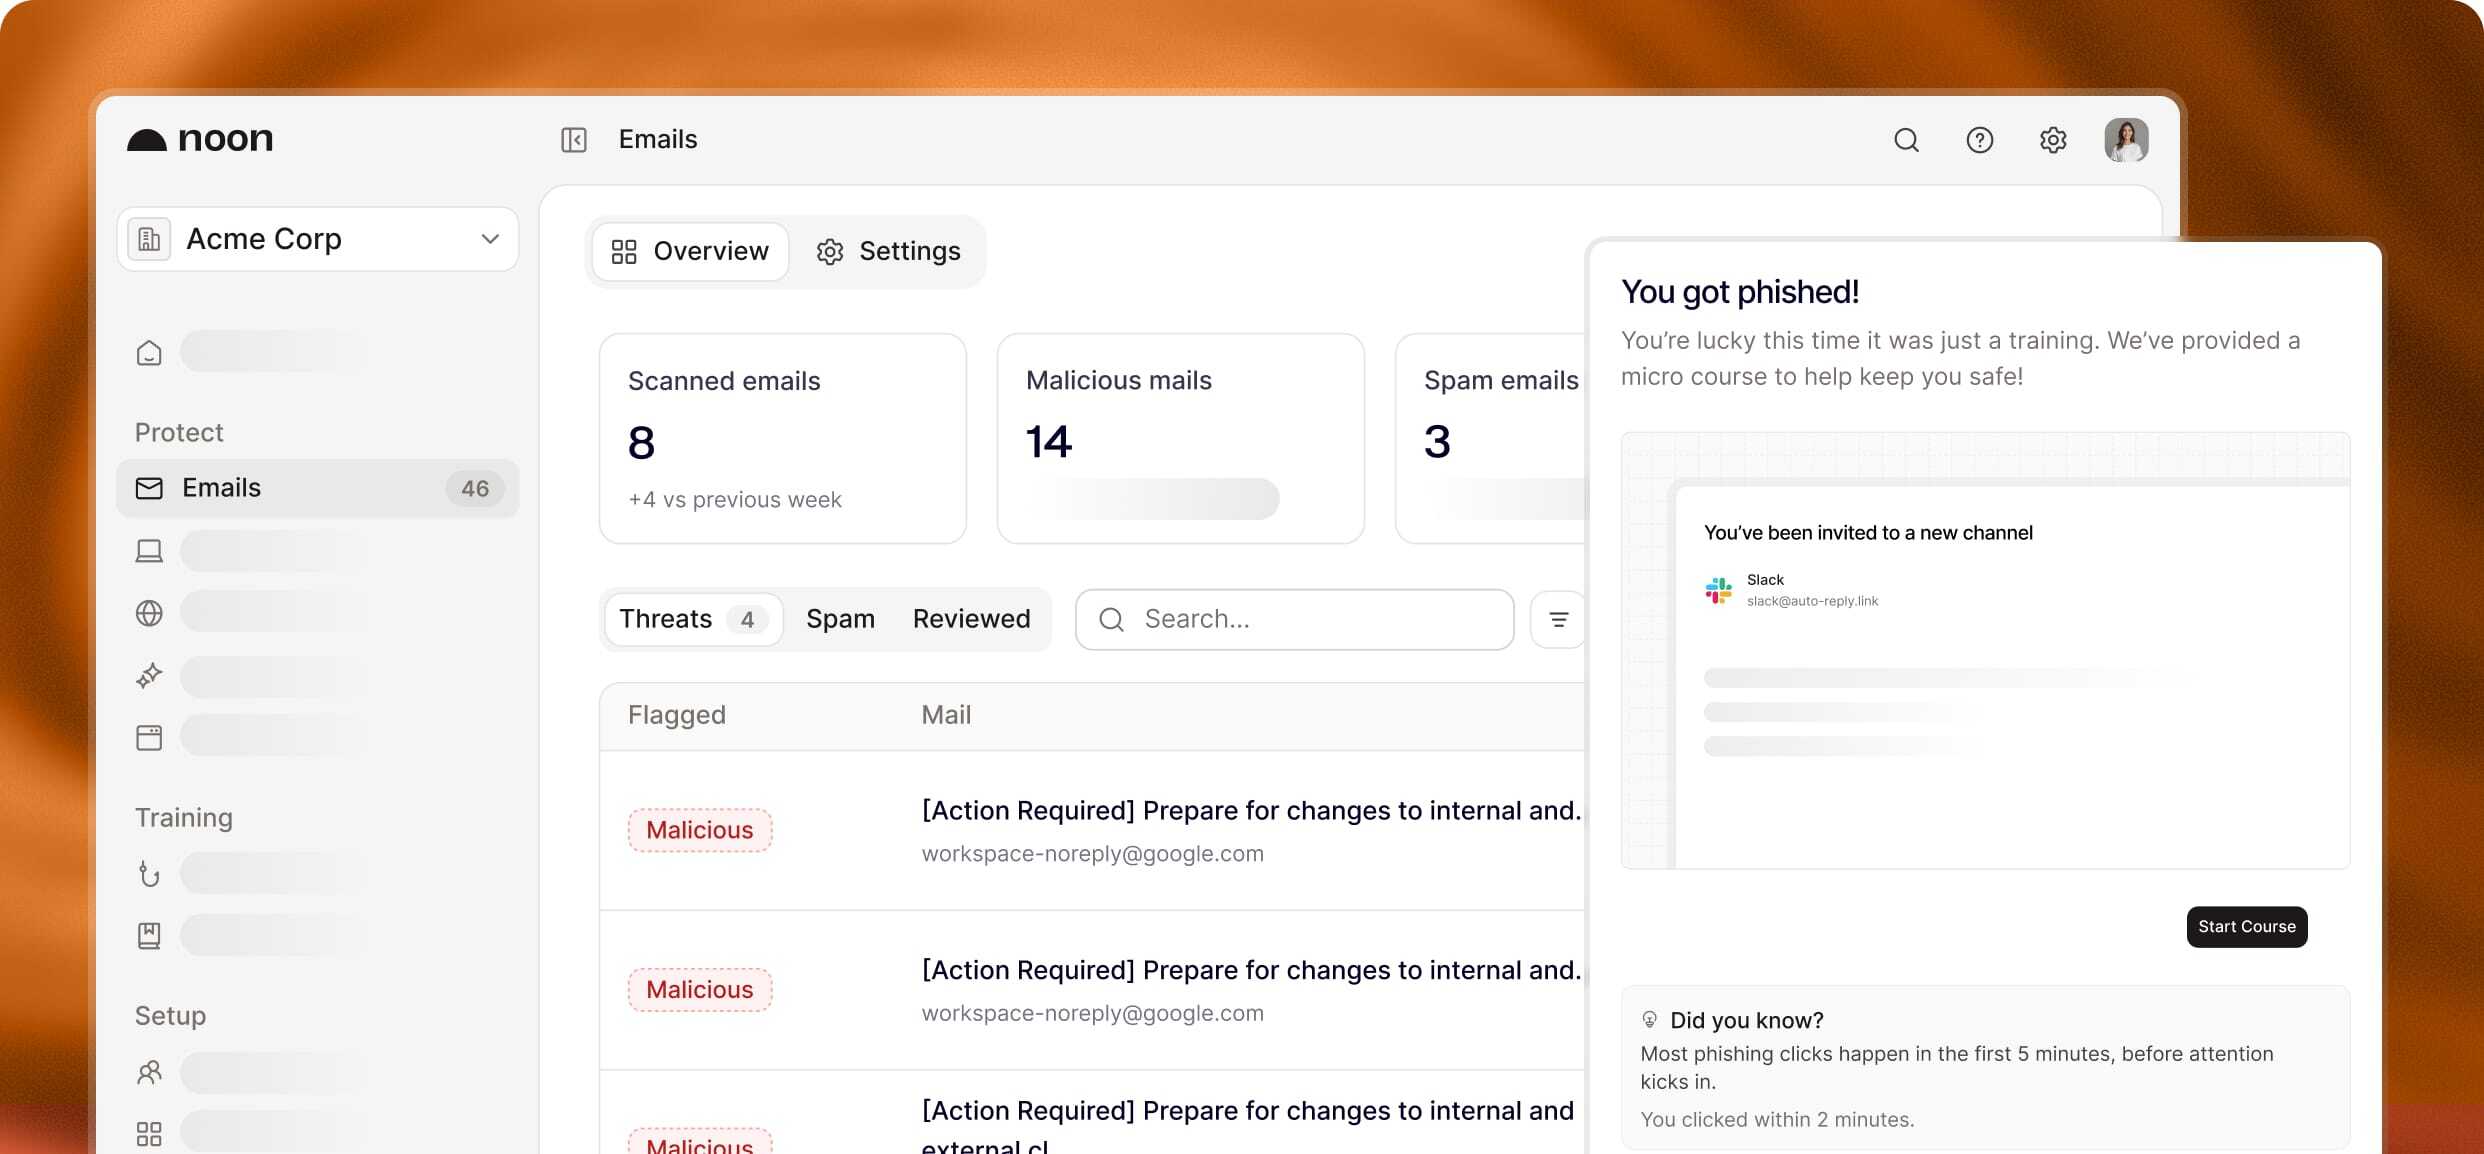
Noon brings email security, device protection, AI governance, as well as complex phishing simulations and training into one platform, covering your team everywhere they work. It’s our answer to “what about everybody else?”
We entered the workforce space because we had the same “this needs fixing” feeling we did when we started Aikido. Aikido started because security tools were so disruptive that developers worked around them, which defeated their purpose. We built something developers would use, and that CISOs approve.
Noon is built the same way. Employees learn from the attacks they’ll face, in the tools they already use, and security teams get one AI-native platform to continuously secure against new threads and old ones accross email, devices, incidents, and AI tools.
What Noon does:
- Email security autonomously detects and removes inbox threats and malicious emails that that traditional filters miss
- AI governance discover what models, MCPs, and AI tools your team uses, keeps sensitive data out of prompts, and enforce safe-use policies by team.
- Device protection covers your new endpoints, protecting employee devices from malicious packages, installs, extensions, agent skills, AI tools, as well as risky websites and apps.
- Training and simulations trains people with realistic and novel attack scenarios - including phishing, vishing, smishing and deepfakes accross channels - personalized by role, behavior, and risk. Lessons delivered in Noon or directly in Slack, Teams, or Google Chat.
Where Noon comes from
Noon starts with two teams already doing this work. In September, Aikido brought on Cyberly, whose team built attack simulations and AI usage visibility, and Outkept, whose team built email security and phishing awareness training. Both founding teams are building Noon with us.

“Aikido has already changed how companies secure their software. With Noon, we’re bringing that same approach to workforce security, backed by Aikido’s global reach.” - Alex Horlach, co-founder of Cyberly.
“AI has fundamentally changed how we need to train and protect employees. What worked five years ago simply isn’t enough anymore. Joining forces with Cyberly and Aikido gives us the opportunity to rethink workforce security and bring a new generation of protection to organizations of all sizes.” - ” Simon Bauwens, co-founder of Outkept.
Welcome to Aikido, Cyberly and Outkept.
The mission? Secure everyone.
{{cta}}


